Designing a Risk-Based Compliance Program: Meeting the 2026 FSC Inspection Criteria
TL;DR:
- Supervisory Shift: The Financial Services Commission (FSC) now targets uncalibrated, generic compliance programs during onsite inspections.
- The New Clock: Static, event-driven profile updates are replaced by mandatory periodic review cycles spanning 1 to 4 years based on risk level.
- Dual-Axis Evaluation: Regulatory audits score firms using a dual matrix that confronts inherent vulnerabilities directly against internal compliance controls.
- The CPF Mandate: Under AMLA 2026, Countering Proliferation Financing (CPF) is a distinct, non-negotiable risk assessment parameter.
Operating a financial or global business structure in Mauritius with a generic “off-the-shelf” manual has become a critical regulatory liability. The Financial Services Commission (FSC) has systematically intensified its supervisory approach, transitioning from standard documentation checks to aggressive, substance-driven inspections.
When supervisory officers enter an organization, they look for empirical proof that the compliance architecture is dynamically matched to actual business volume. A defensive, passive compliance program no longer protects an institution; survival requires a quantitative, risk-based methodology that identifies and isolates operational threats before the regulator detects them.
The New Operational Clock: Fixed CDD Review Cycles
Many compliance officers traditionally updated Customer Due Diligence (CDD) data only when a massive “trigger event” occurred, such as a major structural change in a client’s corporate vehicle. This reactive behavior is now a direct compliance breach.
The regulatory framework mandates that client file updates follow strict, mathematically defined intervals based on their specific risk classification:
- High-Risk Relationships: Require a complete documentation overhaul and screening validation at least once every 12 months.
- Medium-Risk Relationships: Must undergo programmatic updates and transaction reviews every 3 years.
- Low-Risk Relationships: Follow a standard, mandatory refresh timeline every 4 years.
Failing to meet these strict review windows demonstrates a failure of internal corporate controls. If your governance board is still validating files manually without accounting for these automated timelines, your operational structure is fundamentally vulnerable—a baseline gap covered in our comprehensive guide on Corporate Governance in Mauritius: Building Resilient Boards Beyond the Compliance Checkbox.
Dissecting the FSC Onsite Inspection Matrix
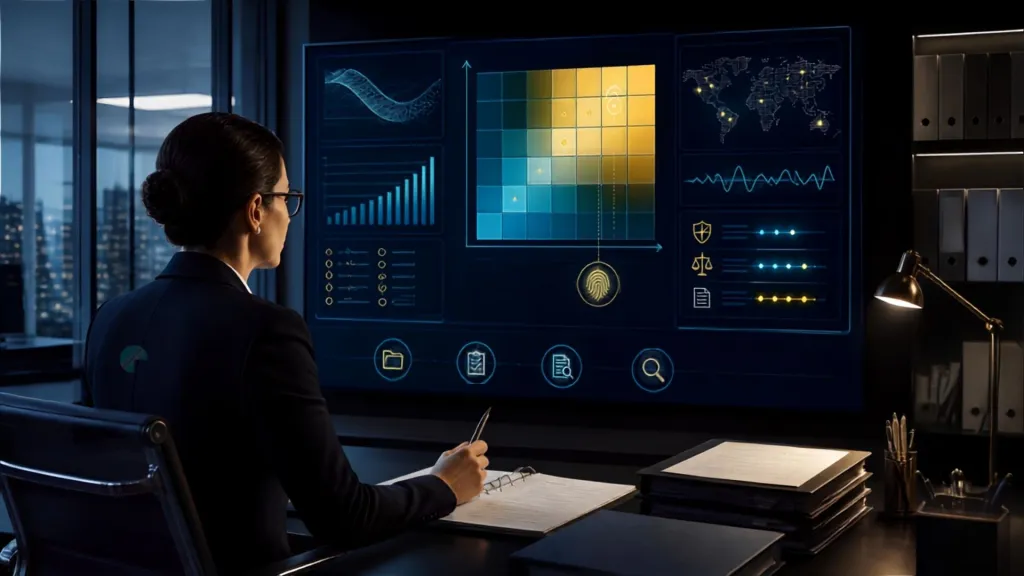
During an inspection, supervisory teams evaluate your framework against a formal two-component matrix designed to compute your organization’s exact residual risk profile.
Understanding how these two axes interact allows a firm to prepare effectively for an audit:
Inherent Vulnerability Factors
This component isolates the baseline risk embedded within your corporate operations, completely separate from your internal defensive measures. Examiners evaluate five distinct operational parameters:
- The exact nature, complexity, and volume of your products and services.
- Your geographical footprint, focusing on high-risk jurisdictions or non-cooperative corridors.
- Your target client segments, specifically measuring the concentration of PEPs or complex trusts.
- Your distribution and delivery channels, identifying reliance on third-party intermediaries.
- The velocity, size, and frequency of cross-border financial transactions.
Internal Compliance Controls
This axis measures the technical strength of your institutional defenses. The inspector evaluates your controls across seven corporate areas, including your internal audit frequency, reporting channels to the MLRO, screening software accuracy, and continuous employee training.
The math is straightforward: if your Component 2 controls cannot structurally counter your Component 1 inherent vulnerabilities, your firm receives a high residual risk rating, triggering immediate regulatory remediation or administrative fines.
The CPF Mandate: Integrating Proliferation Risks
Following recent legislative updates via AMLA 2026, maintaining an AML/CFT program is no longer legally sufficient. Countering Proliferation Financing (CPF) has been codified as a distinct, mandatory pillar of the enterprise risk assessment.
Boards must actively upgrade their transaction monitoring architectures to detect specific, non-traditional financial patterns. This requires implementing real-time screening filters capable of catching dual-use goods data, identifying complex shipping and trade financing networks, and executing immediate asset-freezing protocols against updated domestic and international sanctions lists without any operational lag.
Frequently Asked Questions
What are the mandatory review cycles for client files in Mauritius?
Firms must systematically refresh client documentation based on their risk tier: high-risk files must be updated every 12 months, medium-risk every 3 years, and low-risk every 4 years.
How does the FSC calculate residual risk during an inspection?
The FSC cross-references your inherent vulnerabilities (structural business risks across 5 factors) against your internal compliance controls (7 organizational factors) to compute your final risk score.
What does the CPF pillar require under AMLA 2026?
It requires firms to explicitly assess, map, and mitigate the risk of weapons-proliferation financing, utilizing specialized sanctions screening and dual-use goods detection workflows.
Is an independent compliance audit mandatory for Mauritian license holders?
Yes, the regulatory framework expects periodic, independent reviews of the compliance program to verify that internal risk-scoring controls function accurately in practice.
Your compliance team just spent another week clearing false positives. Was any of that time spent on an alert that actually mattered?
Shifting to a sophisticated, risk-based compliance architecture eliminates administrative backlogs, protects executive directors from individual regulatory liability, and provides a durable credibility signal to international institutional allocators.
The Real Cost of Waiting
If your internal risk matrix has not been calibrated to withstand the dual-axis FSC inspection criteria, your operational license remains exposed.
Ready to close the gap before the FSC finds it? Get in touch with Lead Solution Consultancy.
Sources of this article:
Leave a Reply
Want to join the discussion?Feel free to contribute!